BridgeOpsOne Case Study
AI-powered incident communication platform for IT operations teams
Led platform security assessment and delivery for a dual-product AI SaaS: Chrome extension for real-time incident updates, Academy with OpenAI-graded simulators, config-driven entitlements, and a subscription database ready for Stripe.
- Role
- Platform Security & Full-Stack Engineer
- Timeline
- June 2026, ongoing
- Stack
- Chrome Extension (Plasmo)React 19Node.jsFirebaseFirestoreOpenAIRenderStripe (planned)
- Team
- Solo contractor + client founder
The Problem
BridgeOpsOne helps IT operations teams communicate during incidents with an AI Chrome extension for real-time updates and an Academy of simulators graded by OpenAI. The platform was live but not launch-ready: security gaps exposed OpenAI costs, and the architecture split identity across two Firebase projects.
- Two live products (Chrome extension + Academy website) with separate Firebase projects and auth systems. Same email did not mean same account.
- Critical security gaps before launch: client key in extension bundle, unauthenticated OpenAI grading endpoints, permissive CORS
- No server-driven plan schema. Free-tier limits were hardcoded and bypassable from the UI.
- AI cost exposure: anonymous users could trigger unlimited OpenAI calls on grading and generation routes
- Launch deadline (July 6, 2026) with Chrome Web Store review, pentest follow-ups, and a post-launch Stripe roadmap
- Business requirement: two optional subscriptions (AI Tool + Academy) on one account, not one bundled plan
Platform Architecture
Two products, two Render backends, two Firebase projects, unified at the business level through a subscription schema that treats AI Tool and Academy as separate optional plans on one account.
┌─────────────────────────┬──────────────────────────────────────┐
│ CHROME EXTENSION        │ ACADEMY + SIMULATORS                 │
│ Plasmo + Google OAuth   │ React 19 + Firebase Auth             │
├─────────────────────────┼──────────────────────────────────────┤
│ bridgeopsone-backend    │ bridgeopsone-simulator-api           │
│ .onrender.com           │ .onrender.com                        │
│ OpenAI gpt-4.1-mini     │ OpenAI gpt-4o-mini (grading)         │
│ Firestore: bridgeopsone │ Firestore: bridgeopsone-academy      │
└─────────────────────────┴──────────────────────────────────────┘
                              │
                    bridgeopsone.com (pricing + Stripe Phase E)
                              │
              users/{uid}: aiPlan + academyPlan + usage
Chrome Extension (AI Tool)
Incident updates and timeline generation via OpenAI; Google OAuth; Chrome Web Store
Academy (bridgeopsone-academy.web.app)
AI-graded communication simulators, progress tracking, Firebase Auth
Extension API (Render)
Generate, usage, plans at bridgeopsone-backend.onrender.com
Simulator API (Render)
Grade, sync-profile, plans at bridgeopsone-simulator-api.onrender.com
Pricing (bridgeopsone.com)
Marketing and future Stripe checkout; Academy links here for upgrades
M1 Security Assessment
Milestone 1 delivered a full platform review: repository audit, Firebase/Auth analysis, 20 prioritized security findings, launch readiness verdict, and a phased remediation plan through post-launch Stripe and identity merge.
Critical
3
Client key in extension, unauthenticated grading, public OpenAI test endpoint
High
7
Loose CORS, auth bypass paths, profile sync URL, token in localStorage
Medium
8
No plan enforcement, client-only limits, missing rules in git
Low
2
Documentation drift, duplicate CORS entry
What I Built
- M1 security assessment: 20 findings (3 Critical, 7 High), full architecture map, prioritized remediation through launch and post-launch phases
- Phase A: removed client key from extension; Google OAuth required on all AI routes; strict CORS; Firebase auth on Academy grading; OpenAI test endpoint removed; production smoke-tested on Render + Firebase Hosting
- Phase B: config-driven plan schema (`planConfig.js`), `GET /api/users/me` with usage/limits, email-based anti-rotation for free tier, Google token audience validation, OpenAI output token cap (1024)
- Phase C: Chrome Web Store launch UI with account header, Starter badge, usage counter, Visit Academy link, and prompt-injection hardening on backend
- Phase D: Firestore plan catalog (7 plans, 10 feature keys), dual-product entitlements (`aiPlan` + `academyPlan`), comparison matrix API for bridgeopsone.com pricing page, user migration scripts
- Documented post-launch roadmap (Phases E to I): Stripe checkout, extension billing UI (links only), Academy lab gates, Microsoft login, Firebase merge
Key Features
1. AI incident communication (Chrome extension)
Side-panel tool generates customer-safe incident updates, leadership summaries, and timeline entries via OpenAI on a secured Render backend with per-user rate limits.
2. Academy simulators with AI grading
Communication, audio, and root-cause simulators. OpenAI grades written responses against scenario rubrics; progress saved to Firestore after authenticated submit.
3. Dual-product subscription model
Separate AI Tool and Academy plans on one account. Guest gets 20 AI generations/month and 5 of 25 labs; paid tiers defined in Firestore for admin editing without redeploy.
4. Server-enforced entitlements
All limits enforced on backend only: plan config, usage counters, email anti-rotation, and 403 at limit with upgrade URL pointing to bridgeopsone.com (no payment in extension).
5. Security-first launch hardening
Fail-closed auth, strict Origin checks, deny-all Firestore rules (Admin SDK only), pentest remediations for identity rotation and token audience validation.
6. Structured delivery with client reports
Phased rollout with PDF work reports, smoke-test checklists, and sign-off from security assessment through subscription database.
Academy Screenshot
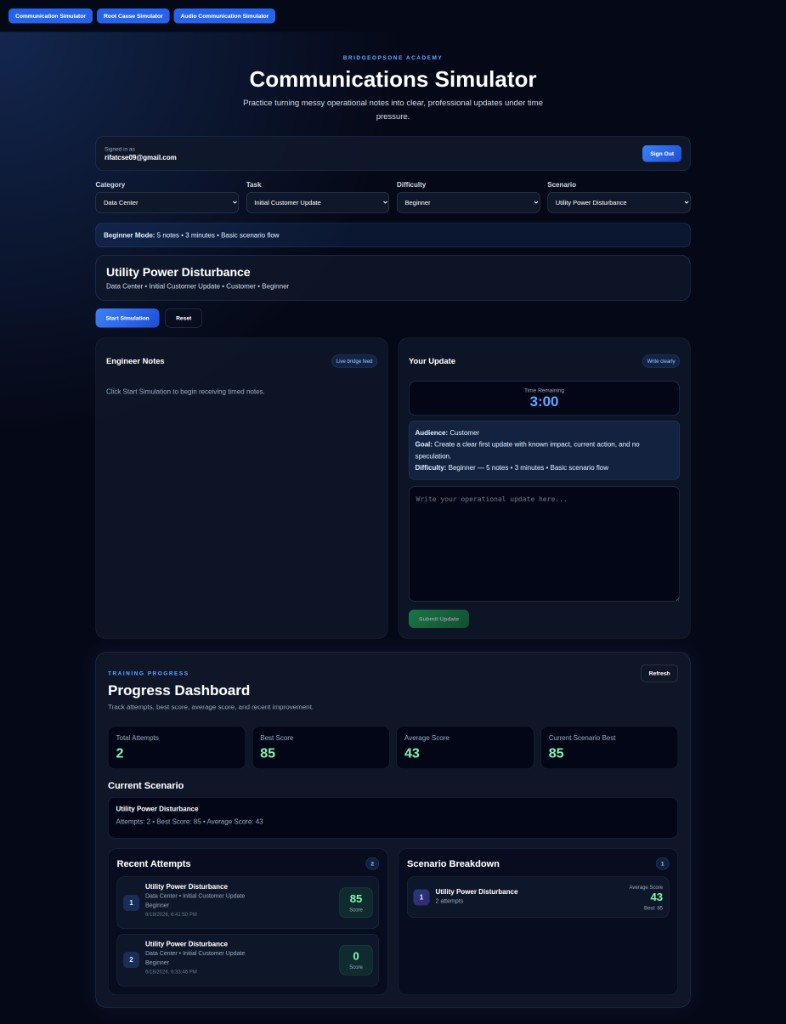
BridgeOpsOne Academy: timed communication simulators with AI grading, scenario selection, and a progress dashboard for NOC and data center training.
Product Demo
Official BridgeOpsOne walkthrough playlist. How the AI Chrome extension and Academy work together for IT operations teams.
How BridgeOpsOne Works
YouTubeChallenges and Solutions
| Challenge | Approach |
|---|---|
| Split identity (Extension OAuth vs Firebase UID) | Documented dual-system architecture; deferred merge to Phase I; enforced limits per product independently until unification |
| OpenAI cost abuse via open endpoints | Require auth on grade/generate; remove test routes; per-user + IP rate limits; max output tokens; client key removed from bundle |
| Free-tier bypass via new Google accounts | Email-based usage tracking in `emailUsage` collection; verified-email requirement; server-side monthly counters |
| Two products, one account, two Stripe subs | Phase D schema: `aiPlan` + `academyPlan` + `stripeSubscriptionIds`; merged entitlements resolver; comparison matrix for pricing page |
| Launch without breaking existing store users | Phased deploy: secure backend first, then store extension update; documented expected 401 for old builds until Phase C publish |
Impact
- Platform secured for July 6 launch: anonymous AI abuse blocked, secrets removed from client bundle, production APIs smoke-tested
- Server-driven plans replace hardcoded limits. Extension and pricing page read from same Firestore catalog.
- Clear roadmap from assessment through subscription database; client has delivery reports for each phase
- Dual-product business model implemented in data layer before Stripe, ready for Phase E checkout on bridgeopsone.com
- Academy live with AI-graded training simulators; extension backend enforces Starter tier with upgrade path to paid plans
- Chrome extension published on Chrome Web Store for NOC, SOC, and data center operations teams
Need an AI SaaS security review or phased launch?
I deliver assessment reports, remediation, OpenAI/Firebase integrations, and milestone-based roadmaps for founders and teams on Upwork or direct.